Home > Xpeak Hurricane > Threat Emulsion & Network Security
Threat Emulation, IPS, IDS & Network Security Testing
Threat Emulation, IPS, IDS & Network Security Testing
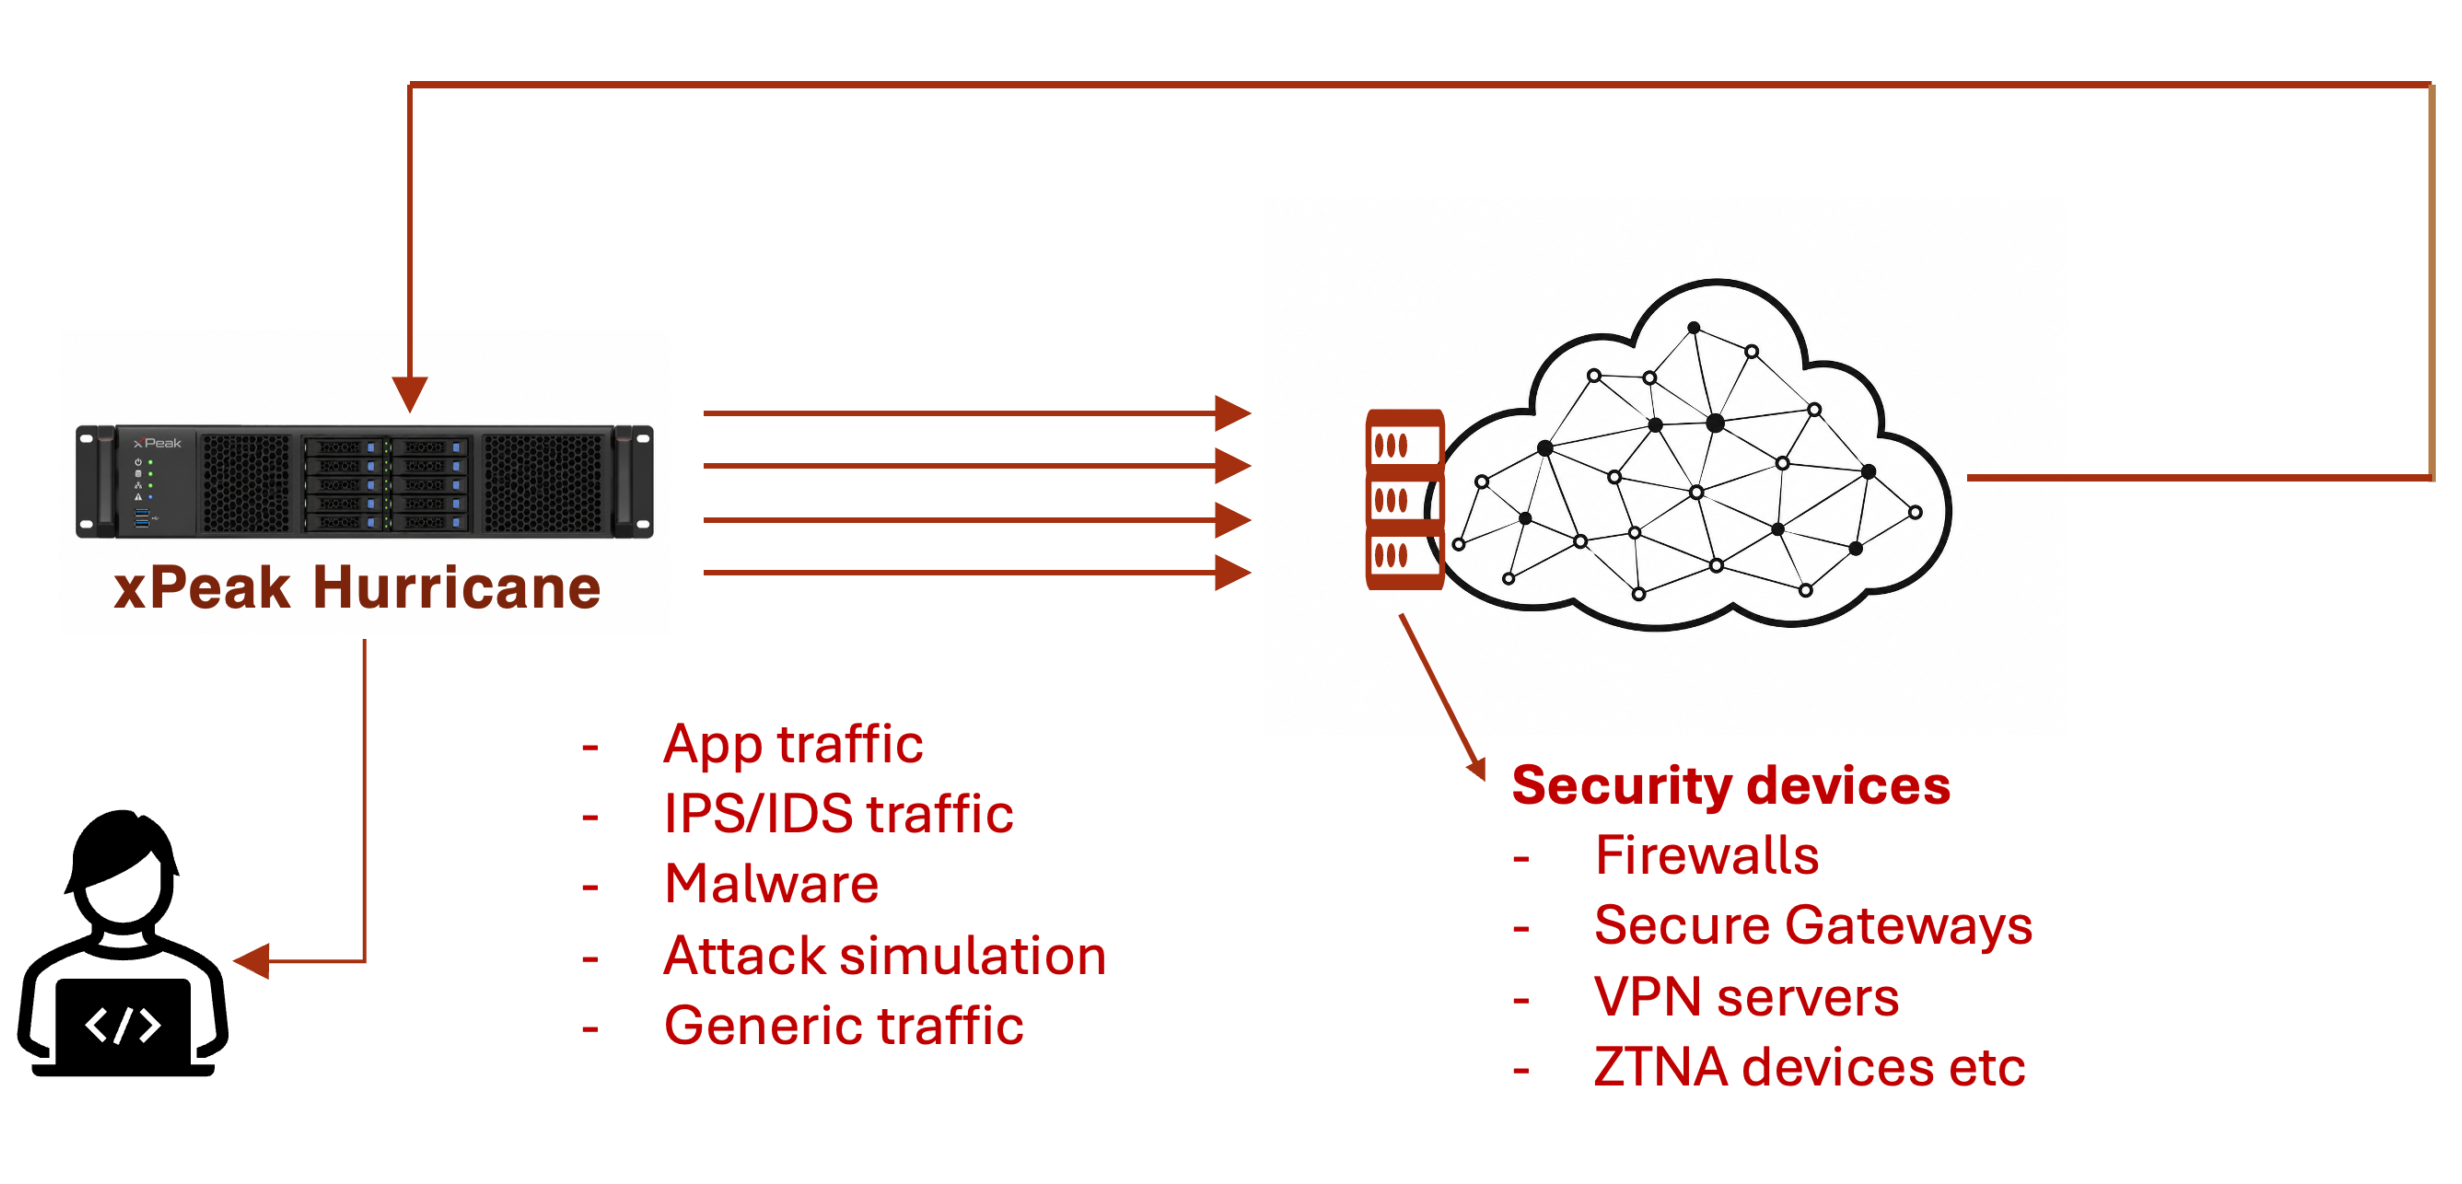
xPeak Hurricane enables network security equipment manufacturers to validate the effectiveness, performance, and resilience of security platforms using realistic application traffic and advanced threat emulation. From IPS/IDS and Deep Packet Inspection engines to Next-Generation Firewalls, Anti-DDoS platforms, and SASE security services, xPeak Hurricane provides comprehensive Layer 4–7 traffic generation and integrated threat simulation to accelerate product development and release validation.
IPS/IDS & DPI Testing
- Validate deep packet inspection and intrusion prevention engines
SASE & L4-7 Traffic Generation
- Generate comprehensive Layer 4–7 traffic with integrated threat simulation to accelerate product development and release validation.
Firewall & Anti-DDoS Validation
- Test Next-Generation Firewalls and Anti-DDoS platforms against real-world attack patterns and threats.
Comprehensive Security Validation
Realistic traffic, advanced threat emulation
xPeak Hurricane combines realistic application traffic with advanced threat emulation, enabling engineering and QA teams to validate both security effectiveness and system performance using a single software-defined platform.
Capabilities highlights:
- CVE-based attack simulation
- Malware and virus emulation
- MITRE ATTACK scenario testing
- Zero-day attack replay
- Threat library validation
- Custom attack scenarios
Use Cases
Detect known and emerging threats, consistently
Ensure that your security platform consistently detects known and emerging threats, while minimizing false positives and false negatives. xPeak Hurricane combines realistic application traffic with advanced threat emulation to validate intrusion detection, malware identification, policy enforcement, and application recognition under real-world operating conditions.
- Signature verification
- IPS rule validation
- IDS alert verification
- False positive analysis
- False negative analysis
- Threat classification validation
- Policy verification
xPeak Advantage
xPeak Hurricane allows security teams to evaluate how detection engines behave when exposed to complex, mixed traffic containing legitimate users, encrypted sessions, malware, DDoS attacks, CVE exploits, and evasive attack techniques. Automated, repeatable test scenarios enable engineering teams to validate new signatures, compare software releases, perform regression testing, and benchmark competing security solutions throughout the product development lifecycle.
Ready to test?
Ready to Validate Your Network at Scale?
See how xPeak Hurricane can help you test application performance, network infrastructure, VPN gateways, firewalls, and SASE platforms with realistic traffic and threat simulation.